
One Click Facebook Conversions API Setup in Hours for Marketers
Practical Facebook Conversions API setup for marketers and business owners. Start with one click or native integrations in a few hours, or hire agency...
The Facebook Conversions API (CAPI) sends conversion events straight from your server, website, or CRM to Meta, filling the measurement gaps browser-based tracking leaves behind.


TL;DR: Quick Answer
Practical Facebook Conversions API setup for marketers and business owners. Start with one click or native integrations in a few hours, or hire agency...
The Facebook Conversions API (CAPI) sends conversion events straight from your server, website, or CRM to Meta, filling the measurement gaps browser-based tracking leaves behind. It works best running alongside the Meta Pixel, not replacing it. Together they give Meta more complete signal, which improves optimisation and reporting accuracy for every campaign you run.
TL;DR:
- A proper CAPI implementation requires generating and sharing a unique event_id between Pixel and server events to prevent duplication.
- Starting with Meta's one-click setup is suitable for most small sites, but larger or more complex funnels benefit from native platform or direct server-to-server integrations.
- Sending essential fields such as event_name, event_time, action_source, and, for web events, event_source_url, is crucial for event acceptance and accurate attribution.
- Hashing personal data like email and phone before transmission and gating data collection on user consent are mandatory to ensure privacy compliance.
- Continual monitoring of event volume and quality scores, along with regular diagnostics, helps maintain a reliable and compliant CAPI setup.
What is the Facebook Conversions API and how does it work?
CAPI is a server-to-server connection. Instead of relying on a browser to fire a tracking pixel, your server sends event data directly to Meta's Graph API endpoint, formatted as https://graph.facebook.com/<api_version>/<pixel_id>/events. The pixel ID in that URL ties the server-side events to the same Meta Pixel (Dataset) you already use for browser tracking, so both feed the same dataset inside Events Manager.
Events sent through CAPI use the same schema as Pixel events. A Purchase, Lead, or AddToCart fired from your server looks structurally identical to one fired from a browser. Meta doesn't distinguish between "server data" and "browser data" once it's ingested. What matters is how each event is described:
- action_source tells Meta where the event originated (website, app, phone call, physical store, chat).
- event_source_url records the page URL tied to a web-based conversion, which helps Meta match the event to the right campaign and creative.
- event_time and event_name anchor the event to a specific moment and action type, matching the naming conventions used by the Pixel.
This is what makes CAPI more resilient than pixel-only tracking. A server call doesn't depend on JavaScript executing, a browser allowing third-party scripts, or a user's device cooperating. The official Meta developer documentation lays out the full parameter structure, and it's worth reading before you write a single line of integration code, because getting the schema right the first time saves you from a messy cleanup later.
Why use CAPI: what signal does it actually recover?
Pixel-only tracking has been losing ground for years, and the causes are well documented. Ad blockers strip pixel scripts before they load. Apple's App Tracking Transparency (ATT) framework limits cross-app tracking on iOS. Intelligent Tracking Prevention (ITP) in Safari throttles cookie lifespans. Each of these, on its own, chips away at how many conversions the Pixel actually sees. Combined, they can leave a meaningful share of real conversions invisible to Meta's ad system.
CAPI doesn't fix browser restrictions. It routes around them. Because the event travels server-to-server, it isn't blocked by browser extensions or affected by cookie expiry. It can also carry conversions the Pixel never sees at all, like a phone call that converts to a sale three days later, or an offline purchase logged in your CRM.
Meta's own positioning is that connecting marketing data directly to its optimisation systems helps advertisers understand ad impact more accurately and reduce wasted spend. Industry coverage of Meta's 2026 rollout of a no-developer one-click CAPI setup points to this signal recovery as the main driver of adoption among smaller advertisers who previously skipped server-side tracking entirely.
What this typically means in practice:
- Better lookalike and broad-audience targeting, because Meta has more confirmed conversions to learn from.
- More accurate reporting in Ads Manager, since events that used to vanish now register.
- Improved bidding for lower-funnel objectives (purchases, leads, qualified appointments), where every missed event has a real cost.
How do Pixel and CAPI work together without double-counting?
Running only the Pixel means you inherit every browser limitation above. Running only CAPI means you lose valuable browser context, like device type, referrer data, and click IDs that help Meta attribute a conversion to the right ad. Meta's own guidance is blunt about this: run both, and let each cover the other's blind spot.
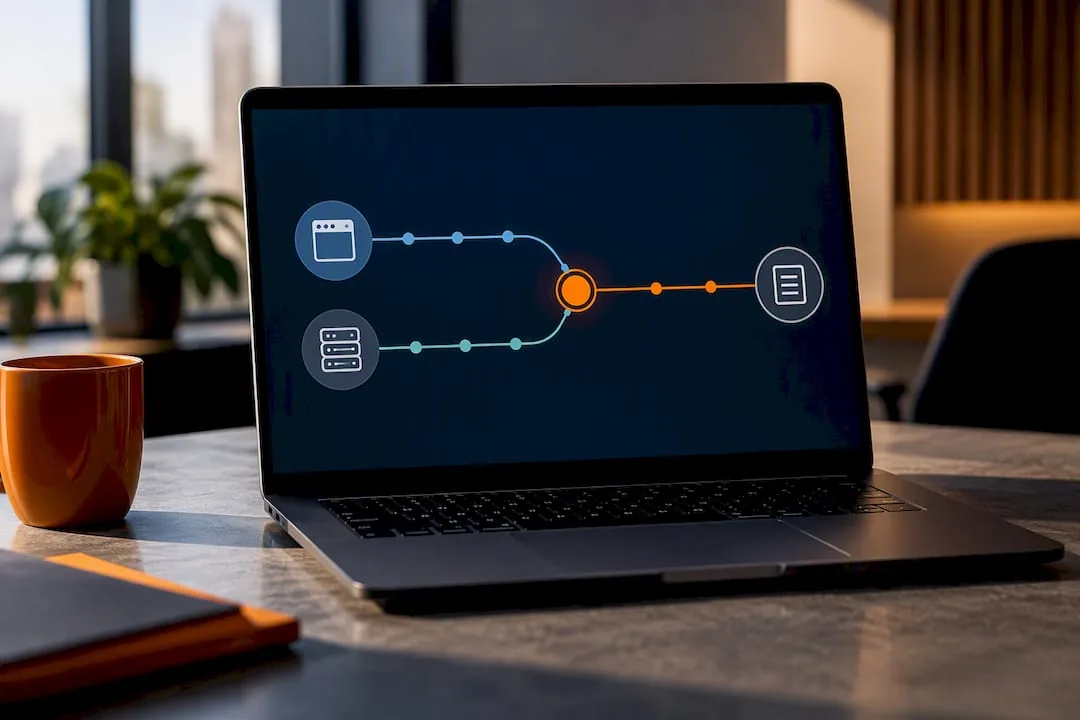
The risk is duplication. If a Purchase event fires from both the browser Pixel and your server at roughly the same time, Meta could count it twice, inflating your conversion numbers and quietly wrecking your cost-per-result data.
The fix is event_id. Generate a unique identifier at the moment of conversion, typically a UUID or order ID, and include that exact same value in both the Pixel event and the CAPI event. Meta uses it to recognise the two events as one and discard the duplicate. This deduplication logic is central to how Meta expects Pixel and CAPI to run together.
- Generate event_id server-side or client-side, but generate it once per conversion.
- Pass the same event_id string to both the Pixel call and the CAPI payload.
- Confirm deduplication is working using Test Events in Events Manager before scaling.
Event Match Quality (EMQ) is the other half of this picture. It's a score inside Events Manager that reflects how well an event's data matches a real Meta user profile. A Purchase event with hashed email, phone, and browser ID attached scores higher than one with just an IP address. Higher EMQ generally means better optimisation, because Meta has more confidence in whose action it's measuring.
Pro Tip: Don't chase a perfect EMQ score on day one. Start by sending the parameters you reliably have (email, phone) and add more identifiers over time as your CRM data quality improves. A stable 6-7 EMQ score with consistent event_id matching beats a fragile 9 that breaks every time a field goes missing.
Which implementation option should you choose?
Not every business needs a custom-built integration. The right approach depends on your platform, technical resources, and how much control you need over the data being sent. Work through these in order:
- Meta's one-click setup. Available for web through Events Manager, this option mirrors your existing Pixel events server-side automatically, with built-in deduplication. Coverage of the 2026 rollout describes it as a genuine no-developer option. You connect it, and Meta handles the rest. The tradeoff is control: it's not configurable, and it only sends what the Pixel already sends. Fine for smaller sites with straightforward funnels; limiting if you need custom event data.
- Native platform integrations. Shopify, WooCommerce, and WordPress plugins increasingly ship with CAPI support built in. These sit between one-click simplicity and full custom control, letting you map specific fields (order value, product IDs) without writing server code yourself.
- Server-side Google Tag Manager (sGTM). A useful middle ground if you already use tag management and want more flexibility than native plugins offer, without committing to a fully custom build.
- Direct server-to-server integration. Full control over every field sent, ideal for businesses with complex funnels, multiple data sources, or a CRM that needs to feed events Meta would otherwise never see. This requires development resources and ongoing maintenance, so reserve it for cases where the other three genuinely fall short.
Before starting any of these, confirm your prerequisites: a verified Business Manager account, an active Pixel or Dataset already collecting browser events, and a System User access token (a long-lived token) generated inside Business Manager settings. Skipping this last step is one of the more common reasons implementations stall halfway through.
If you're running a Meta Ads account for a South African business, start with whichever option matches your platform, and only escalate to a custom build once you've confirmed the simpler route isn't giving you the fields you need.
What fields does the CAPI payload actually need?
Every event you send needs three non-negotiable fields: event_name (Purchase, Lead, AddToCart, and so on), event_time (a Unix timestamp), and action_source (website, app, phone_call, physical_store, other). Miss any of these and Meta rejects the event outright.
For web events specifically, add event_source_url so Meta can tie the conversion back to the page it happened on. Without it, attribution to specific landing pages and ad creatives gets noticeably fuzzier.
Then come the two payload blocks that do the real work:
- user_data: identifiers like email (
em), phone (ph), first name (fn), and last name (ln). Every one of these must be normalised (lowercase, no whitespace, phone numbers in E.164 format) and hashed with SHA-256 before it leaves your server. Meta's API specification documents the exact hashing and formatting rules field by field, and deviating from them is the single most common cause of failed matches. - custom_data: transaction details like value, currency, and content_ids. Currency must follow ISO 4217 formatting (ZAR, USD, EUR), and value should be a plain numeric string, not a formatted price with a currency symbol attached.
The errors that trip up most implementations are predictable: sending event_id in the Pixel call but forgetting it server-side, hashing a field that was already hashed (double-hashing breaks the match completely), or authenticating with a personal access token instead of a System User token. Personal tokens expire, get revoked when an employee leaves, and were never meant for production use. A system user token generated specifically for this integration is the only sound long-term approach.
How do you test and monitor a CAPI implementation?
Shipping a CAPI integration without testing it first is a mistake you'll only catch once the ad account's performance data starts looking wrong. Follow a fixed sequence every time you deploy or change anything:
- Send test events first. Use the Test Events tool inside Events Manager to confirm the payload structure is valid and that hashed fields are actually hashing correctly, before any event touches live campaign data.
- Check Event Match Quality immediately after launch. A newly connected CAPI source often starts with a lower EMQ than your existing Pixel data. Watch it stabilise over the first few days rather than panicking at day one numbers.
- Review diagnostics inside Events Manager weekly. Meta surfaces specific error types, missing parameters, and formatting issues directly in the interface. This is the fastest way to catch a broken field before it costs you a week of skewed optimisation.
- Set an internal alert threshold for event volume. A sudden drop in server-side events, even a partial one, usually signals a token expiry, a broken deployment, or a CRM change upstream. Catching this within a day is far cheaper than catching it a month later in a quarterly report.
Treat this as a recurring maintenance task, not a one-time launch checklist. Integrations quietly break when a website migrates platforms, a token isn't renewed, or a developer changes a field name without checking downstream effects.
How do you handle privacy and consent in a CAPI setup?
CAPI moves more personal data through more systems than pixel tracking alone, which raises the compliance bar rather than lowering it. A few rules are absolute, not optional:
- Hash every personal identifier (email, phone, name) with SHA-256 before it leaves your server. Never send raw PII to Meta's endpoint under any circumstance.
- Gate the entire user_data block on consent. If a visitor hasn't consented to tracking, don't send their hashed data at all, use Meta's data processing options for that event instead.
- Keep a consent record tied to each conversion, so you can demonstrate, if asked, exactly what a user agreed to before their data was processed.
- Apply the same consent gate consistently across every implementation path, whether it's the one-click setup, a native plugin, or a direct integration. A gap in one channel undermines the whole setup.
Data protection expectations vary by jurisdiction, and if you operate across multiple markets, build your consent logic around the strictest standard you're subject to rather than the most convenient one.
What does a real CAPI implementation deliver?
Juicydesigns has seen server-side tracking make the sharpest difference for lead-generation businesses, where a single missed conversion event is a missed sales opportunity, not just a reporting gap.
If you're deciding whether to build this in-house or bring in help, weigh it like this:
- In-house, one-click or native plugin: a few hours of setup, no ongoing developer cost, fine for straightforward funnels.
- In-house, direct integration: requires a developer comfortable with server-side code and ongoing maintenance, best budgeted as an ongoing line item rather than a one-off task.
- Agency-managed setup: faster to launch correctly, useful when your team lacks the technical bandwidth or wants EMQ monitored on a schedule rather than checked occasionally.
Start with the one-click or native path for most standard websites. Escalate to a direct integration only once you've confirmed the simpler route can't carry the specific fields your funnel needs.
Where is server-side tracking heading next?
Server-side APIs aren't a Meta-specific trend, they're becoming the standard measurement layer across every major ad platform, not just this one. If you're only thinking about CAPI in isolation, you're planning one project at a time when you should be planning a measurement roadmap.
Prioritise EMQ and consent-first design over chasing every available field on day one. A clean, consented dataset that scores consistently beats a bloated one that breaks every time a regulation shifts. Treat CAPI as ongoing infrastructure, not a task you finish and forget.
, Cobus
How Juicydesigns can help you implement Conversions API
Juicydesigns is the alternative to hiring a full-time developer for your Meta tracking, without locking you into a long contract to get it done properly.
We handle one-click setups, native platform integrations, and full direct server-to-server builds depending on what your funnel actually needs, then keep monitoring EMQ and event volume so a broken token doesn't quietly cost you a month of ad spend. If you manage ads directly, our Google Ads management packages start from R9,500 per month and pair well with a cleaned-up conversion setup. If you just need a second opinion on your current implementation, get in touch and we'll scope what's missing before you spend another rand on ads running on incomplete data.
Where to go for the official Conversions API documentation
For implementation detail beyond this guide, go straight to primary sources. Meta's developer documentation for the Conversions API covers the full parameter set. The Business Help Center overview explains EMQ diagnostics in plain terms. The server-side API swagger spec on GitHub lists exact field formats and hashing rules for developers building a direct integration.
Sources
- Conversions API - Meta for Developers - Facebook
- Meta's free one-click Conversions API is now live - no developer needed
FAQ
What Is the Facebook Conversions API?
It's a server-side method that sends conversion events, like purchases, leads, and add-to-carts, directly from your server or CRM to Meta, using the same event schema as the Meta Pixel. It's designed to run alongside the Pixel, not replace it, recovering conversions that browser restrictions would otherwise hide.
How Do You Set Up Conversions API on Facebook?
Start in Events Manager, where Meta offers a one-click setup for web that mirrors your existing Pixel events with no developer required, as covered in Meta's 2026 rollout. For more control, use a native platform integration, server-side GTM, or a direct server-to-server build authenticated with a System User access token.
Is the Meta Conversions API Free?
Yes, CAPI itself carries no cost from Meta to send events. If you need it built, monitored, or fully custom-integrated and lack in-house resources, Juicydesigns's once-off SEO audit and setup services start from R8,000 for a similar scoped audit, though CAPI-specific implementation pricing is available on request.
How Do You Get a Facebook Conversions API Access Token?
Generate a System User inside Business Manager's settings and assign it a long-lived access token scoped to your Pixel or Dataset. Never use a personal access token for a production integration, since it expires and ties the connection to one individual's account access.
Is CAPI Better Than the Pixel Alone?
Neither replaces the other; they solve different problems. The Pixel captures rich browser context, while CAPI recovers events lost to ad blockers, iOS App Tracking Transparency, and browser tracking prevention, so running both with a shared event_id gives Meta the most complete picture.
Recommended
- How to Test Facebook Ad Creative (SA Guide 2026)
- Facebook and Instagram Retargeting in South Africa
- How to Set Up a Facebook Business Page Properly (SA 2026)
- Facebook Ads vs Google Ads: Which for SA Business?